How Key Management Helps Organizations Maintain Control Over Encryption Across Multiple Platforms
Introduction
Modern businesses rarely rely on a single technology platform.
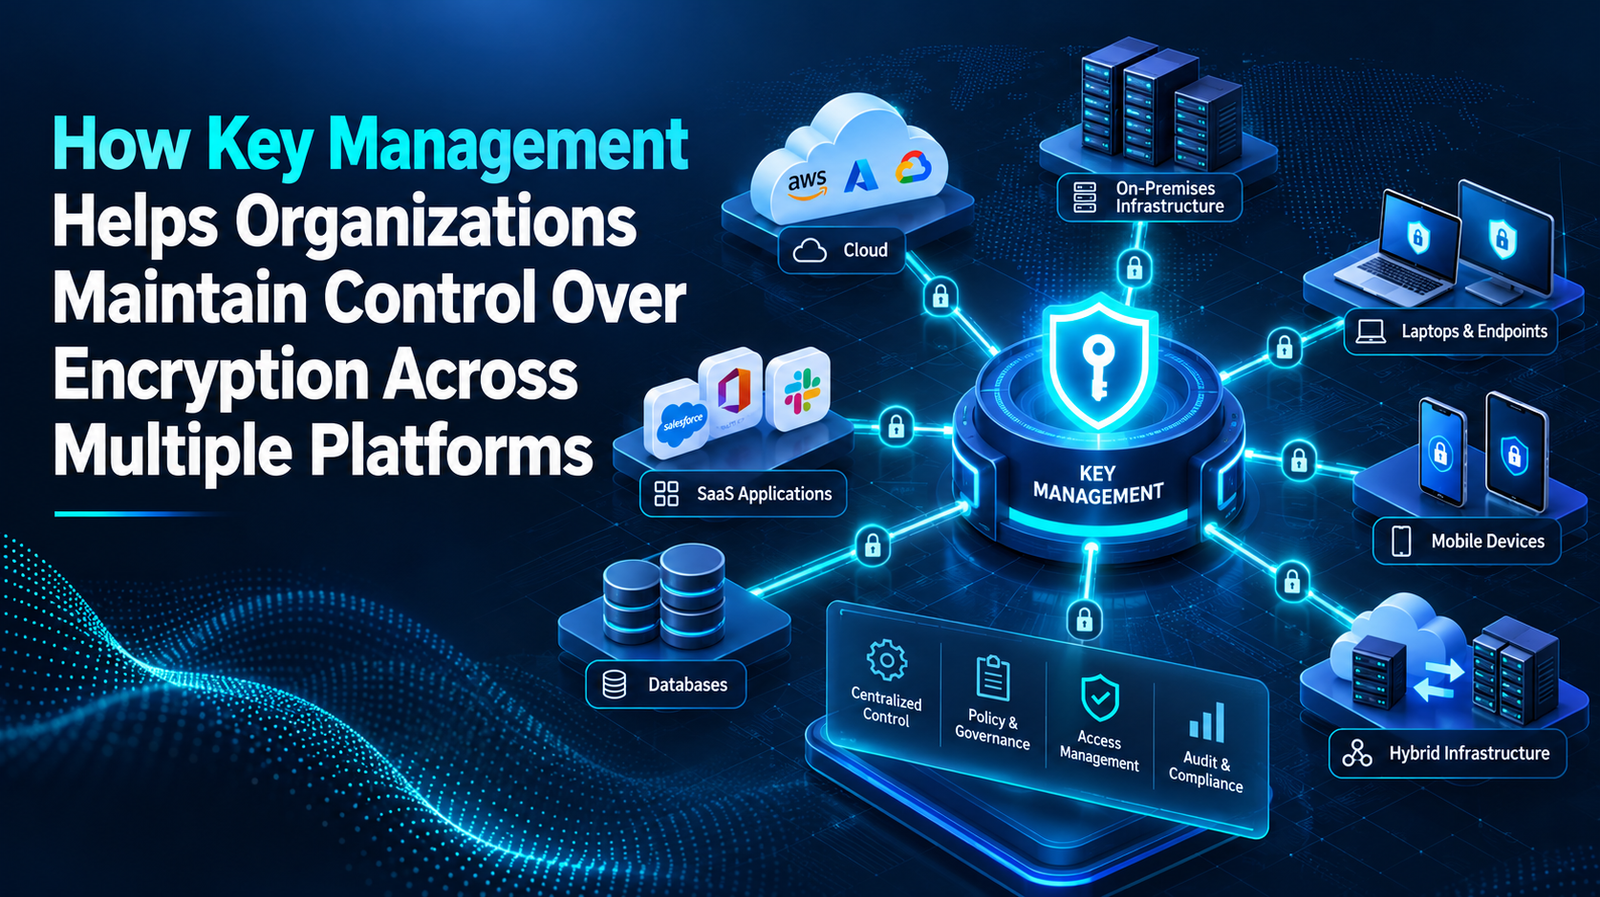
Organizations may use multiple cloud providers, on-premises data centers, SaaS applications, databases, enterprise applications, and hybrid infrastructure.
Each platform may provide different encryption capabilities.
While this flexibility supports business growth, it can make cryptographic key management more complex.
Organizations need to know which keys protect which information, where those keys reside, who can access them, and how they move through their lifecycle.
Without effective controls, enterprises can experience key sprawl, inconsistent policies, excessive permissions, and poor visibility.
This makes centralized Key management increasingly important.
By applying key management in cryptography principles across platforms, organizations can create a more consistent approach to encryption and cryptographic security.
Why Multi-Platform Encryption Creates Challenges
Organizations may encrypt data across:
- Cloud storage
- Cloud databases
- On-premises databases
- Enterprise applications
- Backup systems
- SaaS platforms
- APIs
Each system may introduce different key requirements.
Security teams need to coordinate these requirements without losing visibility.
The Relationship Between Encryption and Key Management
Encryption protects information by transforming it into an unreadable format.
Cryptographic keys control the encryption and decryption process.
Therefore, a strong encryption strategy requires strong Key management.
Organizations should protect keys separately from the data they encrypt.
Key Management in Cryptography
Key management in cryptography covers the complete lifecycle of cryptographic keys.
The lifecycle includes:
- Generation
- Storage
- Distribution
- Access
- Usage
- Rotation
- Backup
- Recovery
- Retirement
- Destruction
Organizations should apply consistent policies throughout this lifecycle.
Maintaining a Centralized Key Inventory
The first step involves gaining visibility.
Security teams should maintain an inventory containing information such as:
- Key identifier
- Owner
- Purpose
- Associated platform
- Protected information
- Lifecycle status
- Rotation schedule
A centralized inventory helps organizations understand their cryptographic environment.
Managing Keys Across Cloud Platforms
Organizations may use multiple cloud platforms for different workloads.
One cloud environment may host customer applications while another supports analytics or backup services.
Each workload may use different encryption mechanisms.
Organizations should maintain consistent Key management policies while accounting for the technical requirements of each platform.
Managing On-Premises Encryption
Traditional data centers may continue to host critical databases and applications.
The keys protecting these systems should form part of the enterprise Key management framework.
Organizations should avoid creating isolated key management processes that security teams cannot easily monitor.
Managing Hybrid Encryption
Hybrid infrastructure combines cloud and on-premises environments.
For example:
Cloud application → On-premises database → Cloud backup
Data may move between all three systems.
Organizations need to maintain appropriate cryptographic controls throughout this process.
Access Control
Organizations should restrict access to cryptographic keys.
The principle of least privilege should apply to users, applications, and services.
Security teams should review permissions regularly.
Access should change when users change roles or applications are retired.
Key Rotation Across Platforms
Organizations should establish key rotation policies.
However, rotating keys across multiple platforms requires careful planning.
Security teams should identify:
- Applications using the key
- Databases depending on it
- Cloud services requiring access
- Backup systems using the key
Organizations should test rotation processes before applying them to production environments.
Key Backup and Recovery
Organizations need reliable recovery processes for critical encryption keys.
If a key becomes unavailable, authorized users may lose access to protected information.
Businesses should protect key backups and restrict recovery permissions.
They should also test recovery procedures regularly.
Avoiding Key Sprawl
Key sprawl can occur when different teams create keys independently.
Organizations can reduce this problem through centralized governance.
Security teams should review the key inventory regularly and identify:
- Unused keys
- Duplicate keys
- Unknown keys
- Keys with excessive permissions
- Keys associated with retired systems
Protecting Application Keys
Applications should not store sensitive cryptographic keys directly in source code.
Instead, they should use approved cryptographic services.
This can reduce the number of locations where sensitive keys exist.
Protecting Database Encryption Keys
Databases often contain highly sensitive information.
Organizations may use encryption to protect database records.
The associated keys should remain protected and separately managed.
Centralized Key management can help maintain consistent lifecycle controls for these keys.
Digital Certificates
Digital certificates rely on cryptographic keys to establish trusted identities.
Organizations should track certificate ownership, expiration, renewal, and private key protection.
Certificate-related keys should form part of the broader Key management strategy.
Monitoring Cryptographic Activity
Organizations should monitor:
- Key creation
- Key access
- Key rotation
- Failed access attempts
- Administrative changes
- Key retirement
Monitoring provides greater visibility across multiple platforms.
Policy Consistency
Different platforms may have different technical capabilities.
However, organizations can establish common enterprise policies.
For example, a policy may require:
- Assigned key ownership
- Least-privilege access
- Defined rotation periods
- Secure backup
- Activity monitoring
- Documented retirement
Technical implementation can vary while the security objectives remain consistent.
Supporting Compliance and Governance
Centralized Key management can help organizations maintain records related to cryptographic controls.
Security teams can document:
- Key ownership
- Access
- Rotation
- Lifecycle status
- Administrative activity
These records can support governance and security reviews.
Common Challenges
Platform Fragmentation
Different systems may use different cryptographic mechanisms.
Inconsistent Policies
Teams may manage keys differently.
Poor Visibility
Security teams may not know where every key resides.
Key Sprawl
Large environments can accumulate unnecessary keys.
Complex Rotation
Multiple systems may depend on the same key.
Best Practices
Organizations should:
- Maintain a centralized cryptographic inventory
- Define enterprise Key management policies
- Assign key ownership
- Apply least privilege
- Separate keys from protected information
- Establish rotation procedures
- Automate appropriate lifecycle activities
- Monitor key activity
- Protect backups
- Test recovery
- Review permissions
- Retire obsolete keys
Conclusion
Organizations increasingly operate across multiple technology platforms.
Encryption helps protect information across these environments, but cryptographic keys require dedicated security controls.
Key management in cryptography provides the lifecycle framework for controlling these keys.
Effective Key management can help organizations maintain visibility, consistent access policies, rotation procedures, recovery capabilities, and governance across cloud, on-premises, and hybrid infrastructure.
By establishing centralized policies while accommodating platform-specific requirements, enterprises can maintain stronger control over encryption and build a more consistent cryptographic security framework.